416,214
Files scanned on the first read-only pass, 13 November
Case study · Client · Hacked-site cleanup
rgbcorp.eu is a Madrid creative studio running WordPress and WooCommerce. Luis, from the studio, gave us permission to name rgbcorp.eu here. On 8 November 2026 an attacker reached the live site. The most likely way in was an older, unmaintained sub-shop on the same hosting account. Forensic confirmation still depends on the hosting provider’s server access logs. We contained the 13 affected pages and cleaned the account. On 13 November those pages were back as normal live pages (HTTP 200). The main site had no downtime during that day’s clean-up.
From the 13 November 2026 clean-up.
Files scanned on the first read-only pass, 13 November
WordPress installs on one shared system account, all in scope
One more older site, out of scope and left untouched
Legacy plugin copies removed from the web root
Main-site pages restored from a temporary Cloudflare 403 to HTTP 200
Main-site downtime during the 13 November clean-up
WordPress admin logins rotated, plus 8 security keys or salts on each of the 7 installs
Database users rotated (7 active WordPress configs tested, plus 5 legacy users)
Dangerous or plugin paths still blocked at the Cloudflare edge (HTTP 403)
From 8 November, a temporary Cloudflare 403 held the 13 public pages so visitors and Google would not see the injected gambling spam. After the 13 November clean-up we checked them with a browser and with Googlebot. The HTML was clean, with no gambling spam and no PHP errors. Then we reopened them as HTTP 200.
Held from 8 to 13 November. Checked with a browser and with Googlebot, then back live on 13 November.
Main site during the 13 November clean-up: 0 downtime. The homepage and the rest of the unblocked site stayed up. The 13 pages came back the same night, once we had finished and checked the clean-up.
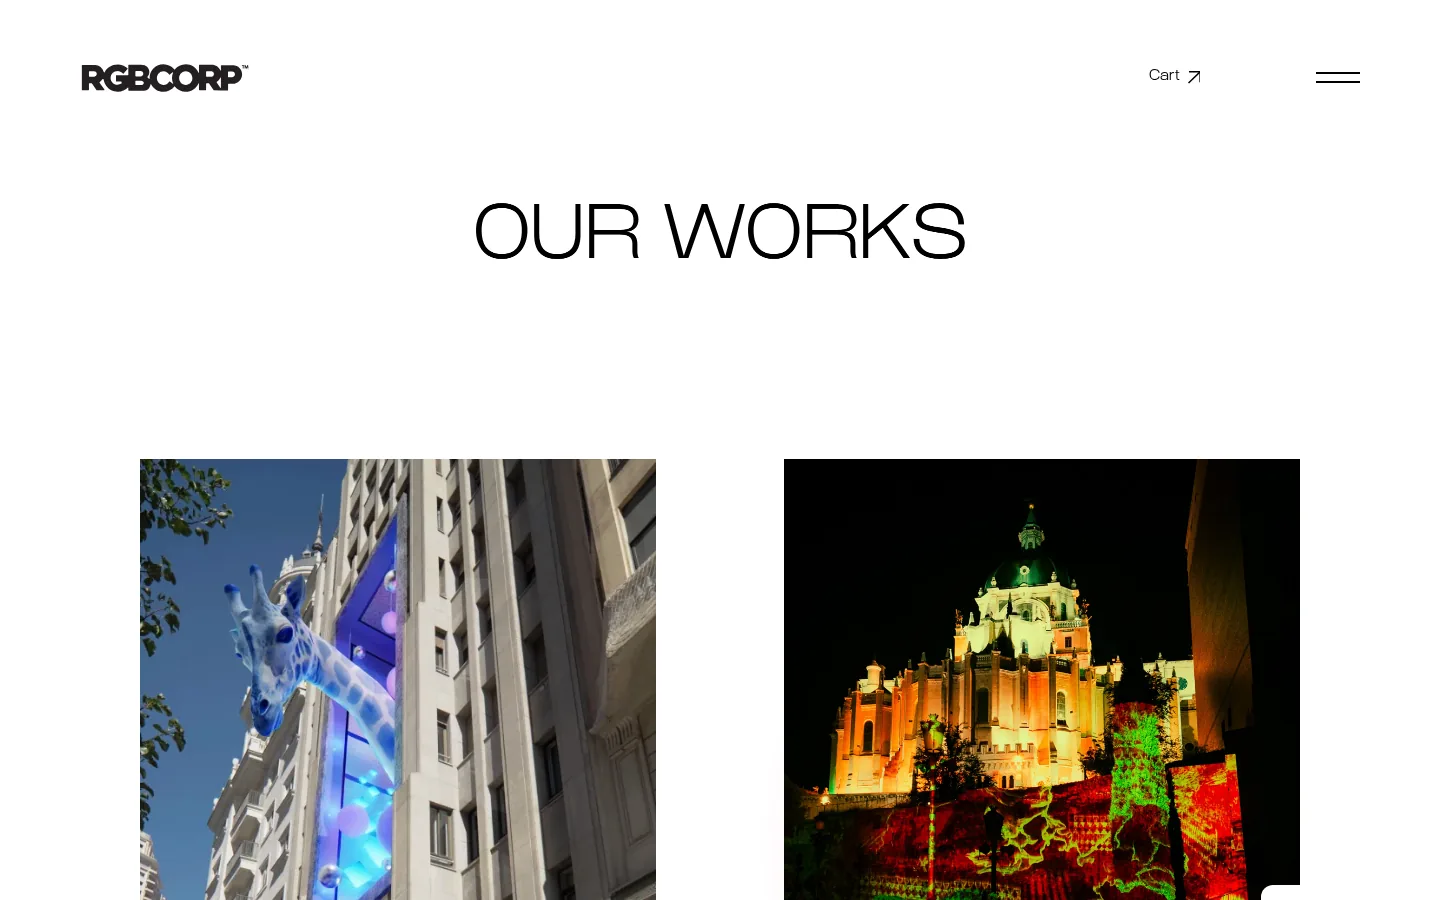
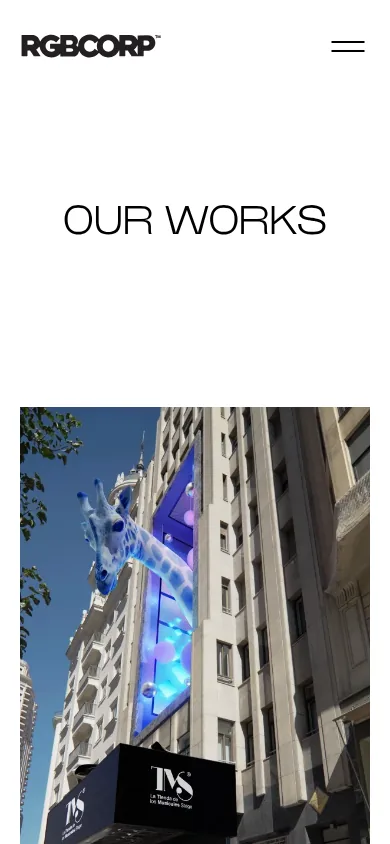
The restored live site on 13 November 2026: the public Works page at 1440 and 390 px wide, with the cookie banner closed.
All of the studio’s WordPress installs share one hosting account. We leave out usernames, folder paths and filenames, so this page can’t serve as a map for the next attacker.
Cloudflare edge
A temporary rule first held the 13 public pages at 403. Once those pages were checked clean and reopened, 19 dangerous or plugin paths stayed blocked at the edge, so traffic through Cloudflare can’t reach them.
Origin · one shared hosting account
The most likely entry point is an older, unmaintained sub-shop on that shared account. It was first compromised in March 2025 through an outdated file-manager plugin. To confirm it forensically, we still need the hosting provider’s server access logs. Until then, it is our most likely explanation, not a proven one.
These are the five steps of our Hacked-site cleanup service, in the order we publish them. We followed them for rgbcorp.eu on 13 November 2026, with the client’s approval.
A full hosting backup from before the attack, dated 8 November, was already in place before we changed anything. On 13 November we also took a fresh 81.9 GB full backup and verified that it could be restored.
What we found: web-shell files, an auto-login dropper, an unauthorised caching plugin and hidden gambling links. The gambling links sat in an unmaintained legacy sub-shop, first compromised in March 2025 through an outdated file-manager plugin. We quarantined all of this instead of deleting it blind. Leftover file-manager tooling went into quarantine too. So did 430 MB of outdated plugin copies still in the web root, plus 8 pirated or nulled plugin copies.
We took the compromised sub-shop offline, removed the outdated file-manager plugin from every copy on the account, tightened file permissions, and kept the dangerous paths blocked at Cloudflare. That older sub-shop is the most likely entry point. Forensic confirmation still depends on the hosting provider’s server access logs.
We updated WordPress where licences allowed. Not every plugin could be updated: the page-builder and multilingual plugins are licence-locked and need the client’s own licences. We rotated 8 security keys or salts on each of the 7 installs. We also rotated 12 WordPress admin logins, 12 database users (7 active WordPress configs updated and connection-tested, plus 5 legacy users), and the FTP and control-panel passwords. Two accounts the client asked us to leave untouched were left as they were. Finally, we closed every open session.
We reopened the 13 main-site pages at the Cloudflare edge and checked that visitors and Googlebot both got clean live pages. We re-checked the 19 dangerous paths, and they are still blocked. The full re-scan ran with the malware already in quarantine and found 0 live malicious files. The remaining pattern hits were known false positives. That full re-scan came before the final password rotation. After hardening, and again after the edge restore, we ran targeted live HTTP and database-connection checks. A short written report sets out what we cleaned, what stays blocked, and what is still with the client and the host.
The studio first came to Remote Mend for a live-site rebuild and audit. The rebuilt site went live on 2 November, with a before/after report dated the same day.
Less than a week later, an attacker dropped web-shell files, planted an auto-login dropper, installed an unauthorised caching plugin and temporarily replaced 13 live site pages with gambling spam. The most likely way in was an older, unmaintained sub-shop on the same hosting account. Forensic confirmation still depends on the hosting provider’s server access logs.
Remote Mend’s first response removed a persistence backdoor and the 13 spam page folders, and put a temporary Cloudflare rule in front of those 13 paths so visitors and Google would not see the spam.
A fuller investigation found two things. The original web-shell files and the hidden gambling links on the old sub-shop were still there. And the sub-shop’s first compromise went back to March 2025, through an outdated file-manager plugin and a rogue account. With the client’s approval we ran the five-step clean-up the same day: a 416,214-file read-only scan, an 81.9 GB backup verified restorable, quarantine rather than blind deletion, a re-scan with 0 live malicious files, credential rotation, and the 13 pages restored to HTTP 200. The main site had 0 downtime during that clean-up.
To be precise: not every plugin could be updated, because some are licence-locked. The clean full re-scan ran after the malware quarantine and before the final password rotation. After that, we ran targeted live HTTP and database-connection checks after hardening and after the 13 pages were restored at the edge.
Ask for a quote. We’ll tell you what we can see and what the work would involve. Scope and price depend on what was affected.
Ask for a quote →